AI Security · AI Governance · GRC
I help organisations understand and manage cybersecurity and AI risk, in plain English.
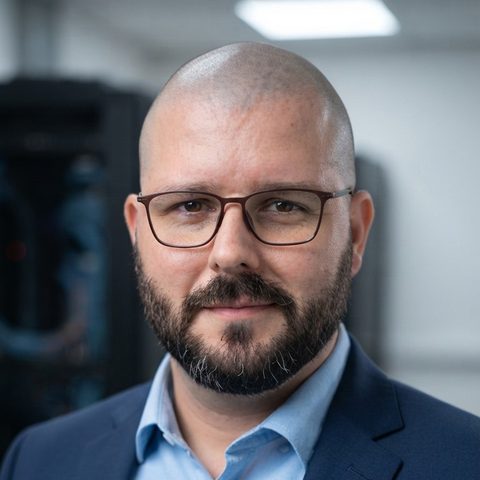
I’m Danilo Stojkovic, founder of PeritumAI. I work on what the EU AI Act and other rules mean for a business, where its AI use is exposed, and what to fix first. Available for freelance and advisory work.
Research and articles
Everything I publish now lives at PeritumAI
My articles, free guides and white papers on AI security, AI governance and GRC moved to peritumai.com in November 2026. Old dsperitum.com article links take you straight to the new versions.
About
Security and AI rules, turned into steps people can follow
My focus is governance, risk and compliance (GRC), AI governance and AI security: the EU AI Act, NIST AI RMF, ISO/IEC 42001, NIST CSF 2.0, ISO/IEC 27001 and GDPR. I take long regulations and standards and turn them into short, prioritised actions for teams that don’t have a compliance department.
At PeritumAI I publish plain-English guidance and research, and I’m building an AI-assisted pipeline that collects public AI-security incidents and turns them into short, human-reviewed risk reports.
Before that I spent years as a direct-response copywriter, which is why I can take a 100-page regulation and explain what it means for your business.
Why GRC
I did the operational side of it for 8+ years before I had the label. Running front offices and night operations in Serbia and Malta (EU), I:
- Gave and removed system and key-card access by role (least privilege in practice)
- Ran nightly reconciliations and audits, investigated discrepancies and kept clean audit trails
- Handled passports, IDs and payment cards daily under GDPR and PCI-relevant rules
- Led incident response and escalation as duty manager
- Wrote SOPs and policies from zero, trained teams and checked they were followed
- Managed third parties: booking platforms, payment processors and suppliers
Consulting
Freelance and advisory work
I take on a small number of engagements through PeritumAI. The work is readiness and advisory, not certification audits.
AI risk snapshot
A quick look at the AI tools and systems you use, where data could leak or be misused, and the few fixes that matter most.
AI governance readiness
An AI inventory, risk classification and gap review against the EU AI Act, NIST AI RMF or ISO/IEC 42001, with a plan you can act on.
AI policy and EU AI Act preparation
AI acceptable-use policy, roles and controls, AI literacy for staff, and the documents customers and regulators ask for.
Fractional advisor
Ongoing part-time help with AI security, AI governance and GRC questions, security questionnaires and policy updates.
Experience
CV
-
Aug 2026 – present · Remote
Founder, AI Security & Governance Consultant · PeritumAI (formerly DS Peritum)
- Plain-English articles and guides on AI security, AI governance and GRC, including a free guide, AI Governance, Made Simple, and a white-paper series
- Translate the EU AI Act, NIST AI RMF, NIST CSF 2.0, ISO/IEC 27001 and GDPR into practical, prioritised steps for non-technical teams
- Building an AI-assisted incident pipeline (local LLM) that analyses public security incidents into short, human-reviewed risk reports
- Readiness and advisory consulting on AI risk, AI policy and EU AI Act preparation
-
Feb 2023 – present · Belgrade, Serbia
Front Office Manager / Sales & Event Manager · Calisi Hotel
- Built the front-office operation from launch: SOPs, operational controls, staffing and workflows
- Access control: create and remove system accounts and key-card access by role
- Data protection: guest IDs, passports and payment cards under GDPR and PCI-relevant handling
- Duty manager for incidents and escalations; coordinate third parties (booking platforms, payment processors, suppliers)
- Recruited, trained and lead a team of 8
-
Jul 2020 – Aug 2022 · Kopaonik, Serbia
Night Auditor, then Sales & Marketing Associate · Gorski Hotel & Spa
- Nightly financial reconciliation and audit on Oracle/Fidelio PMS; investigated and corrected discrepancies; kept audit trails
- Sole manager on duty overnight: decisions, incident handling and escalation
-
Jan 2018 – Oct 2019 · Malta (EU)
Night Manager · Gillieru Harbour Hotel and Porto Azzurro Hotel
- Ran overnight front-office, night-audit and security operations at two hotels at the same time
- Physical security, access control and incident response; personal and payment data in an EU (GDPR) environment
-
2008 – 2019 · Niš, Serbia
Earlier · business owner, sales, copywriting
- Founder and owner of a cleaning services business (2013–2019): pricing, contracts, invoicing, staff, suppliers
- Sales consultant and team manager, Hyla Network (2008–2014); freelance direct-response copywriter
Frameworks
EU AI Act · NIST AI RMF · ISO/IEC 42001 · NIST CSF 2.0 · ISO/IEC 27001 · GDPR · OWASP Top 10 for LLM Applications
Certifications
CompTIA Security+ (SY0-701), in progress
Microsoft SC-900, in progress
IAPP AIGP, planned
Languages
English (C2) · Serbian (native) · Slovak (B2) · Polish (B2)
How I work: I use AI tools every day for research and building, including local models for anything that should stay private, and I check every output against the original source.
Contact
Let’s talk
Questions about AI security, AI governance or compliance, a project, or a role? Email me and I’ll reply personally, usually within a day or two.